Comprehensive User Authentication
2FA (TOTP, SMS, email), biometric login (Face ID, Touch ID), FIDO2 hardware key support (YubiKey, Titan), and anti-phishing protections.
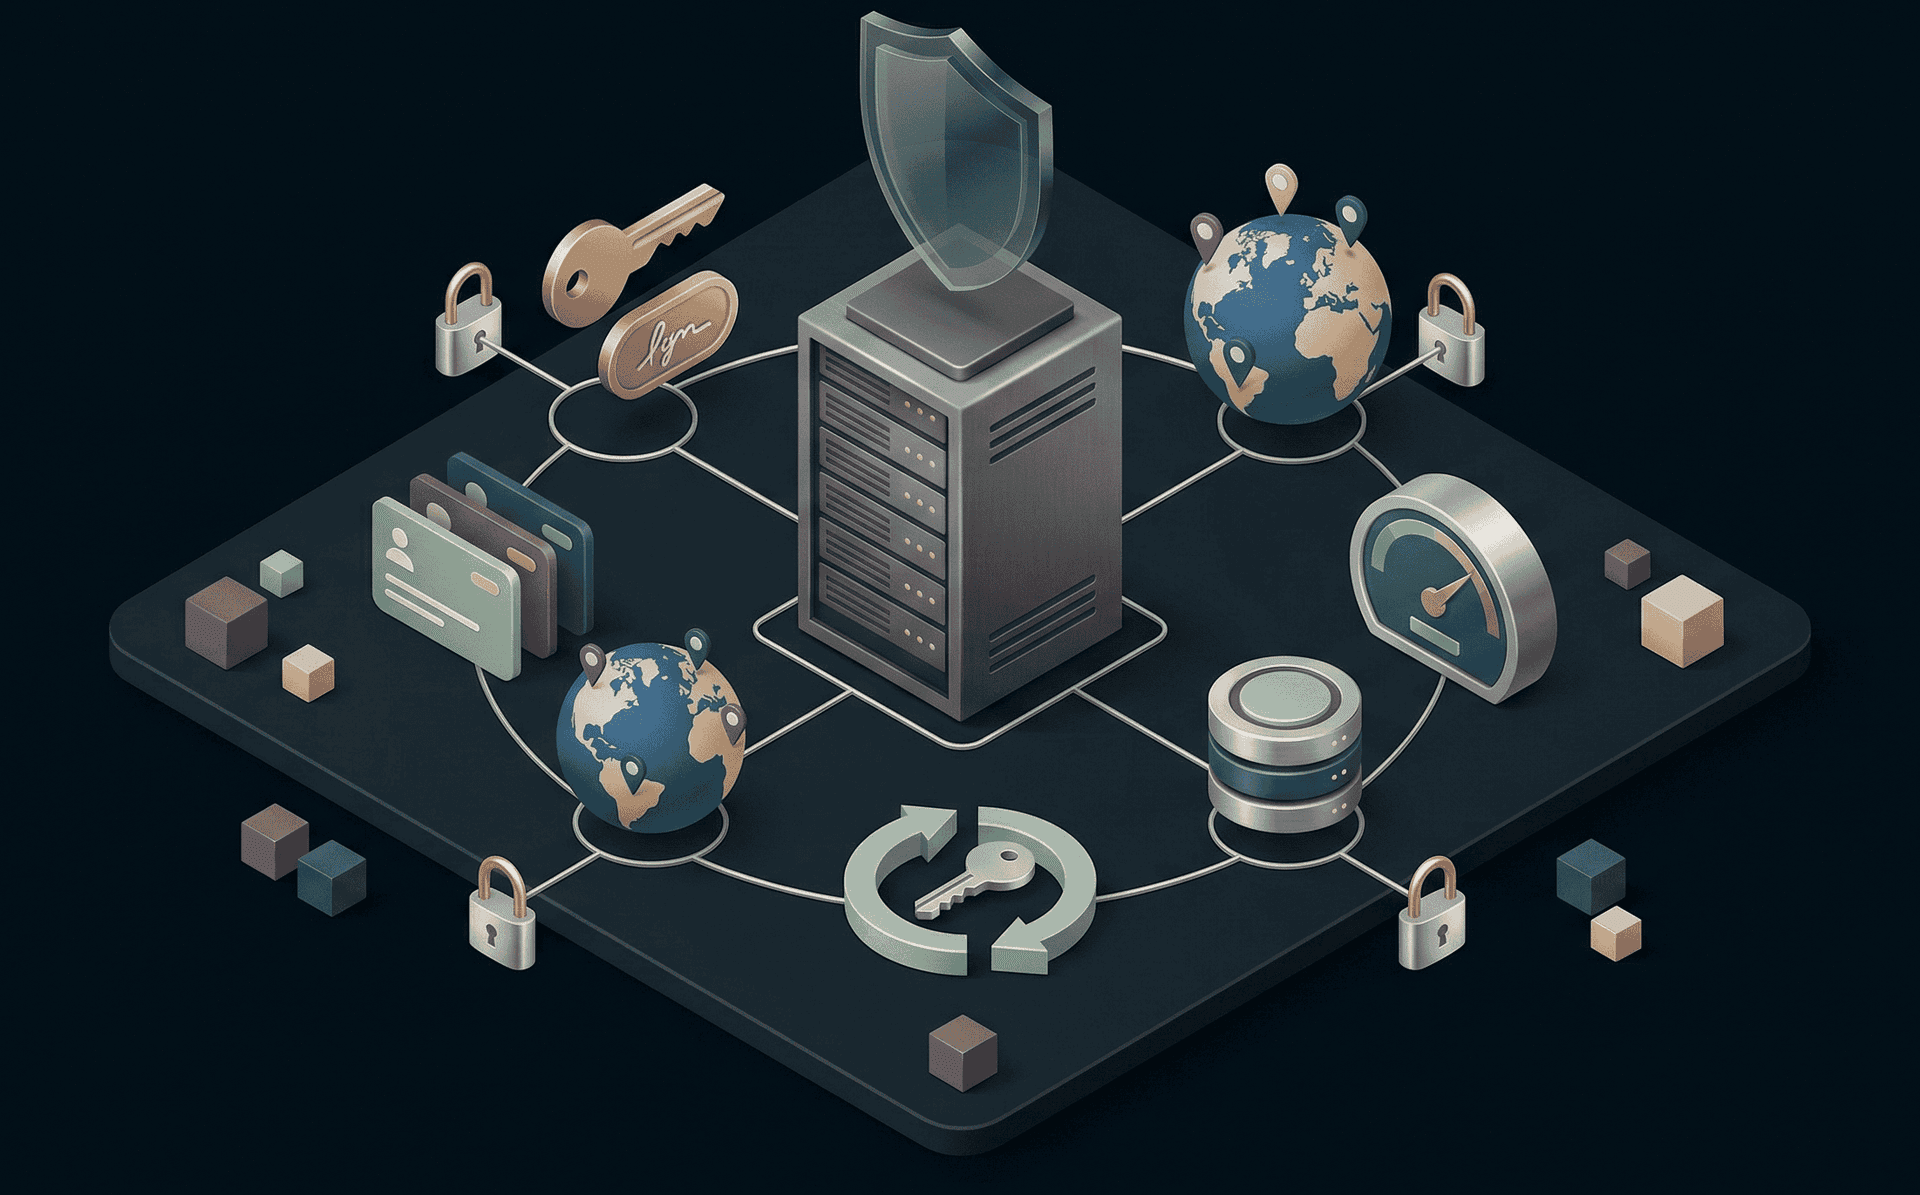
Institutional-Grade Asset Protection. One breach destroys years of platform growth. The security framework protects across every layer, asset custody, trading integrity, account access, withdrawal fraud, infrastructure resilience, and incident response.
95%+ cold storage with HSM, multi-sig, and geographically distributed keyholders. Operator-exclusive fund control ensures platform developers cannot access stored assets.
End-to-end encryption via TLS 1.3 in transit, AES-256 at rest, HMAC-SHA256 on API, and PGP on email. Access hardened through MFA (TOTP, SMS, email, biometric, FIDO2 hardware keys), scoped API keys with HMAC signing, IP whitelisting.
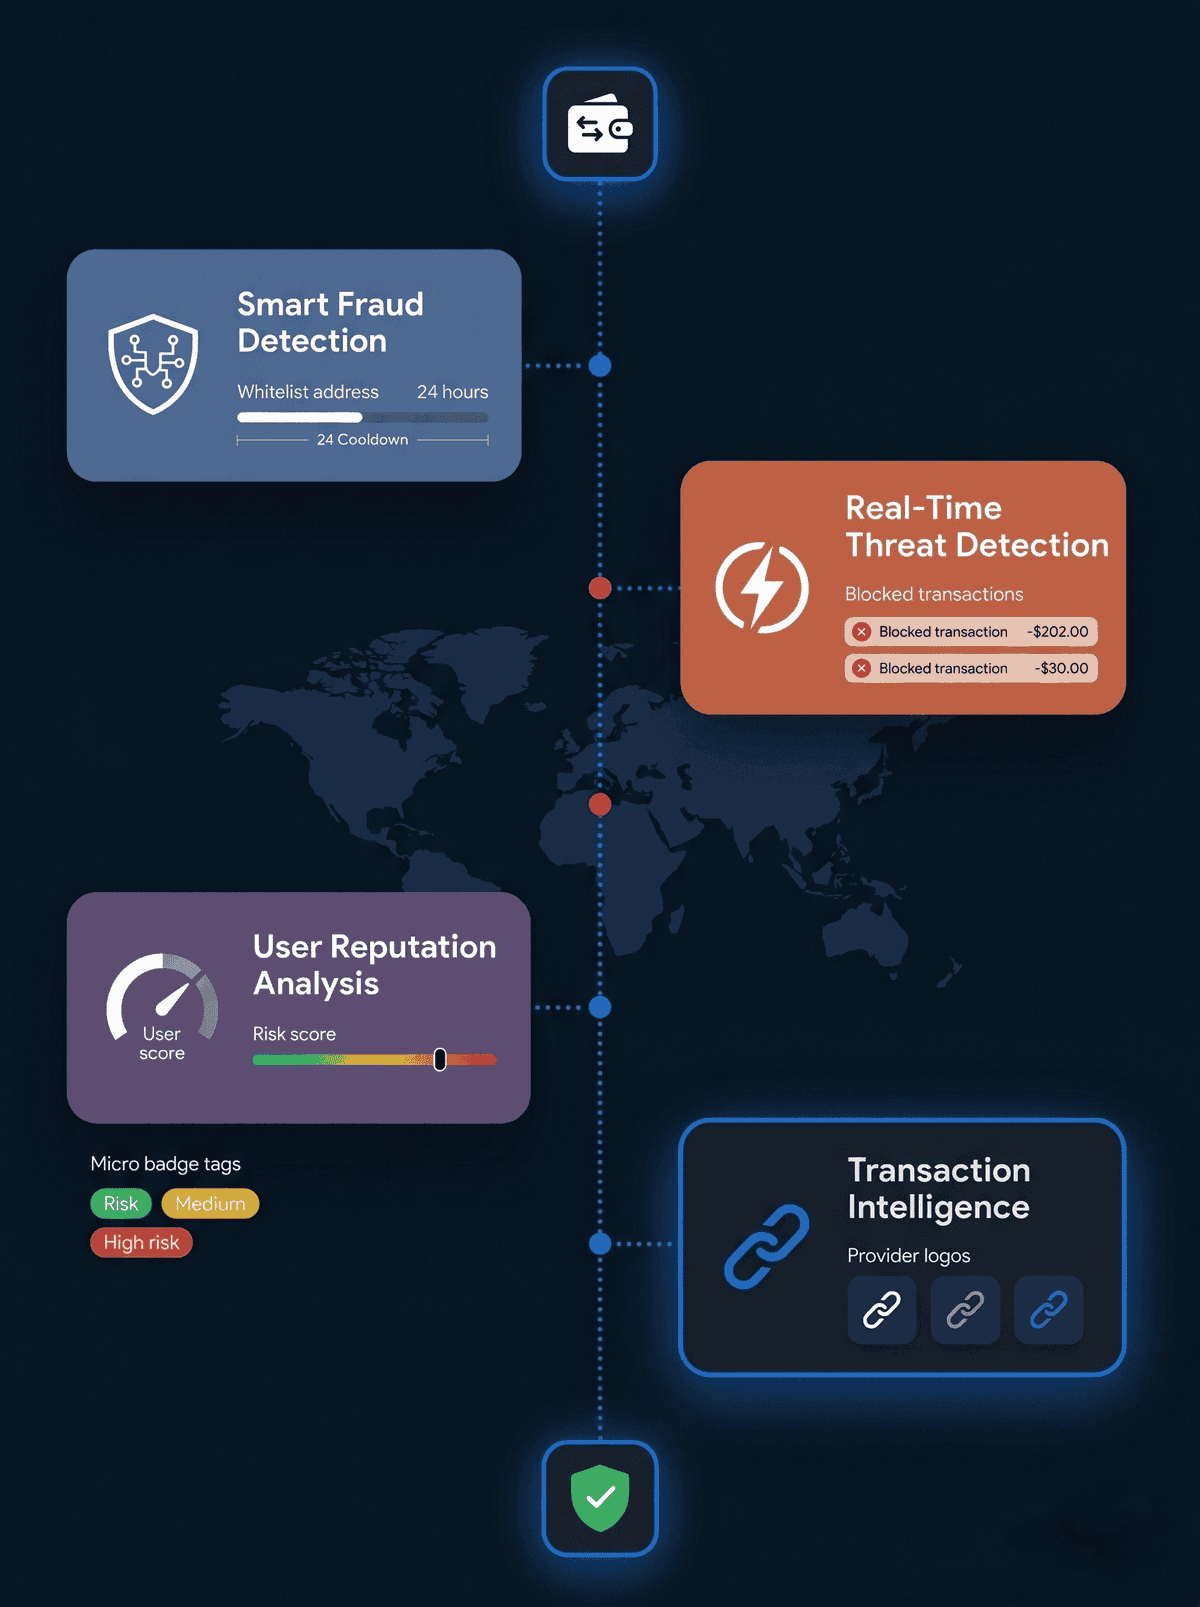
Real-time trading surveillance covers arbitrage protection, wash trading detection, and risky asset management. Behavioral fraud detection, user reputation scoring.
OFAC, EU, and UN sanctions screening with Chainalysis/Elliptic integration ensures regulatory coverage. Security posture validated through third-party audits, penetration testing, bug bounty programs, and a 24-hour critical patch SLA.
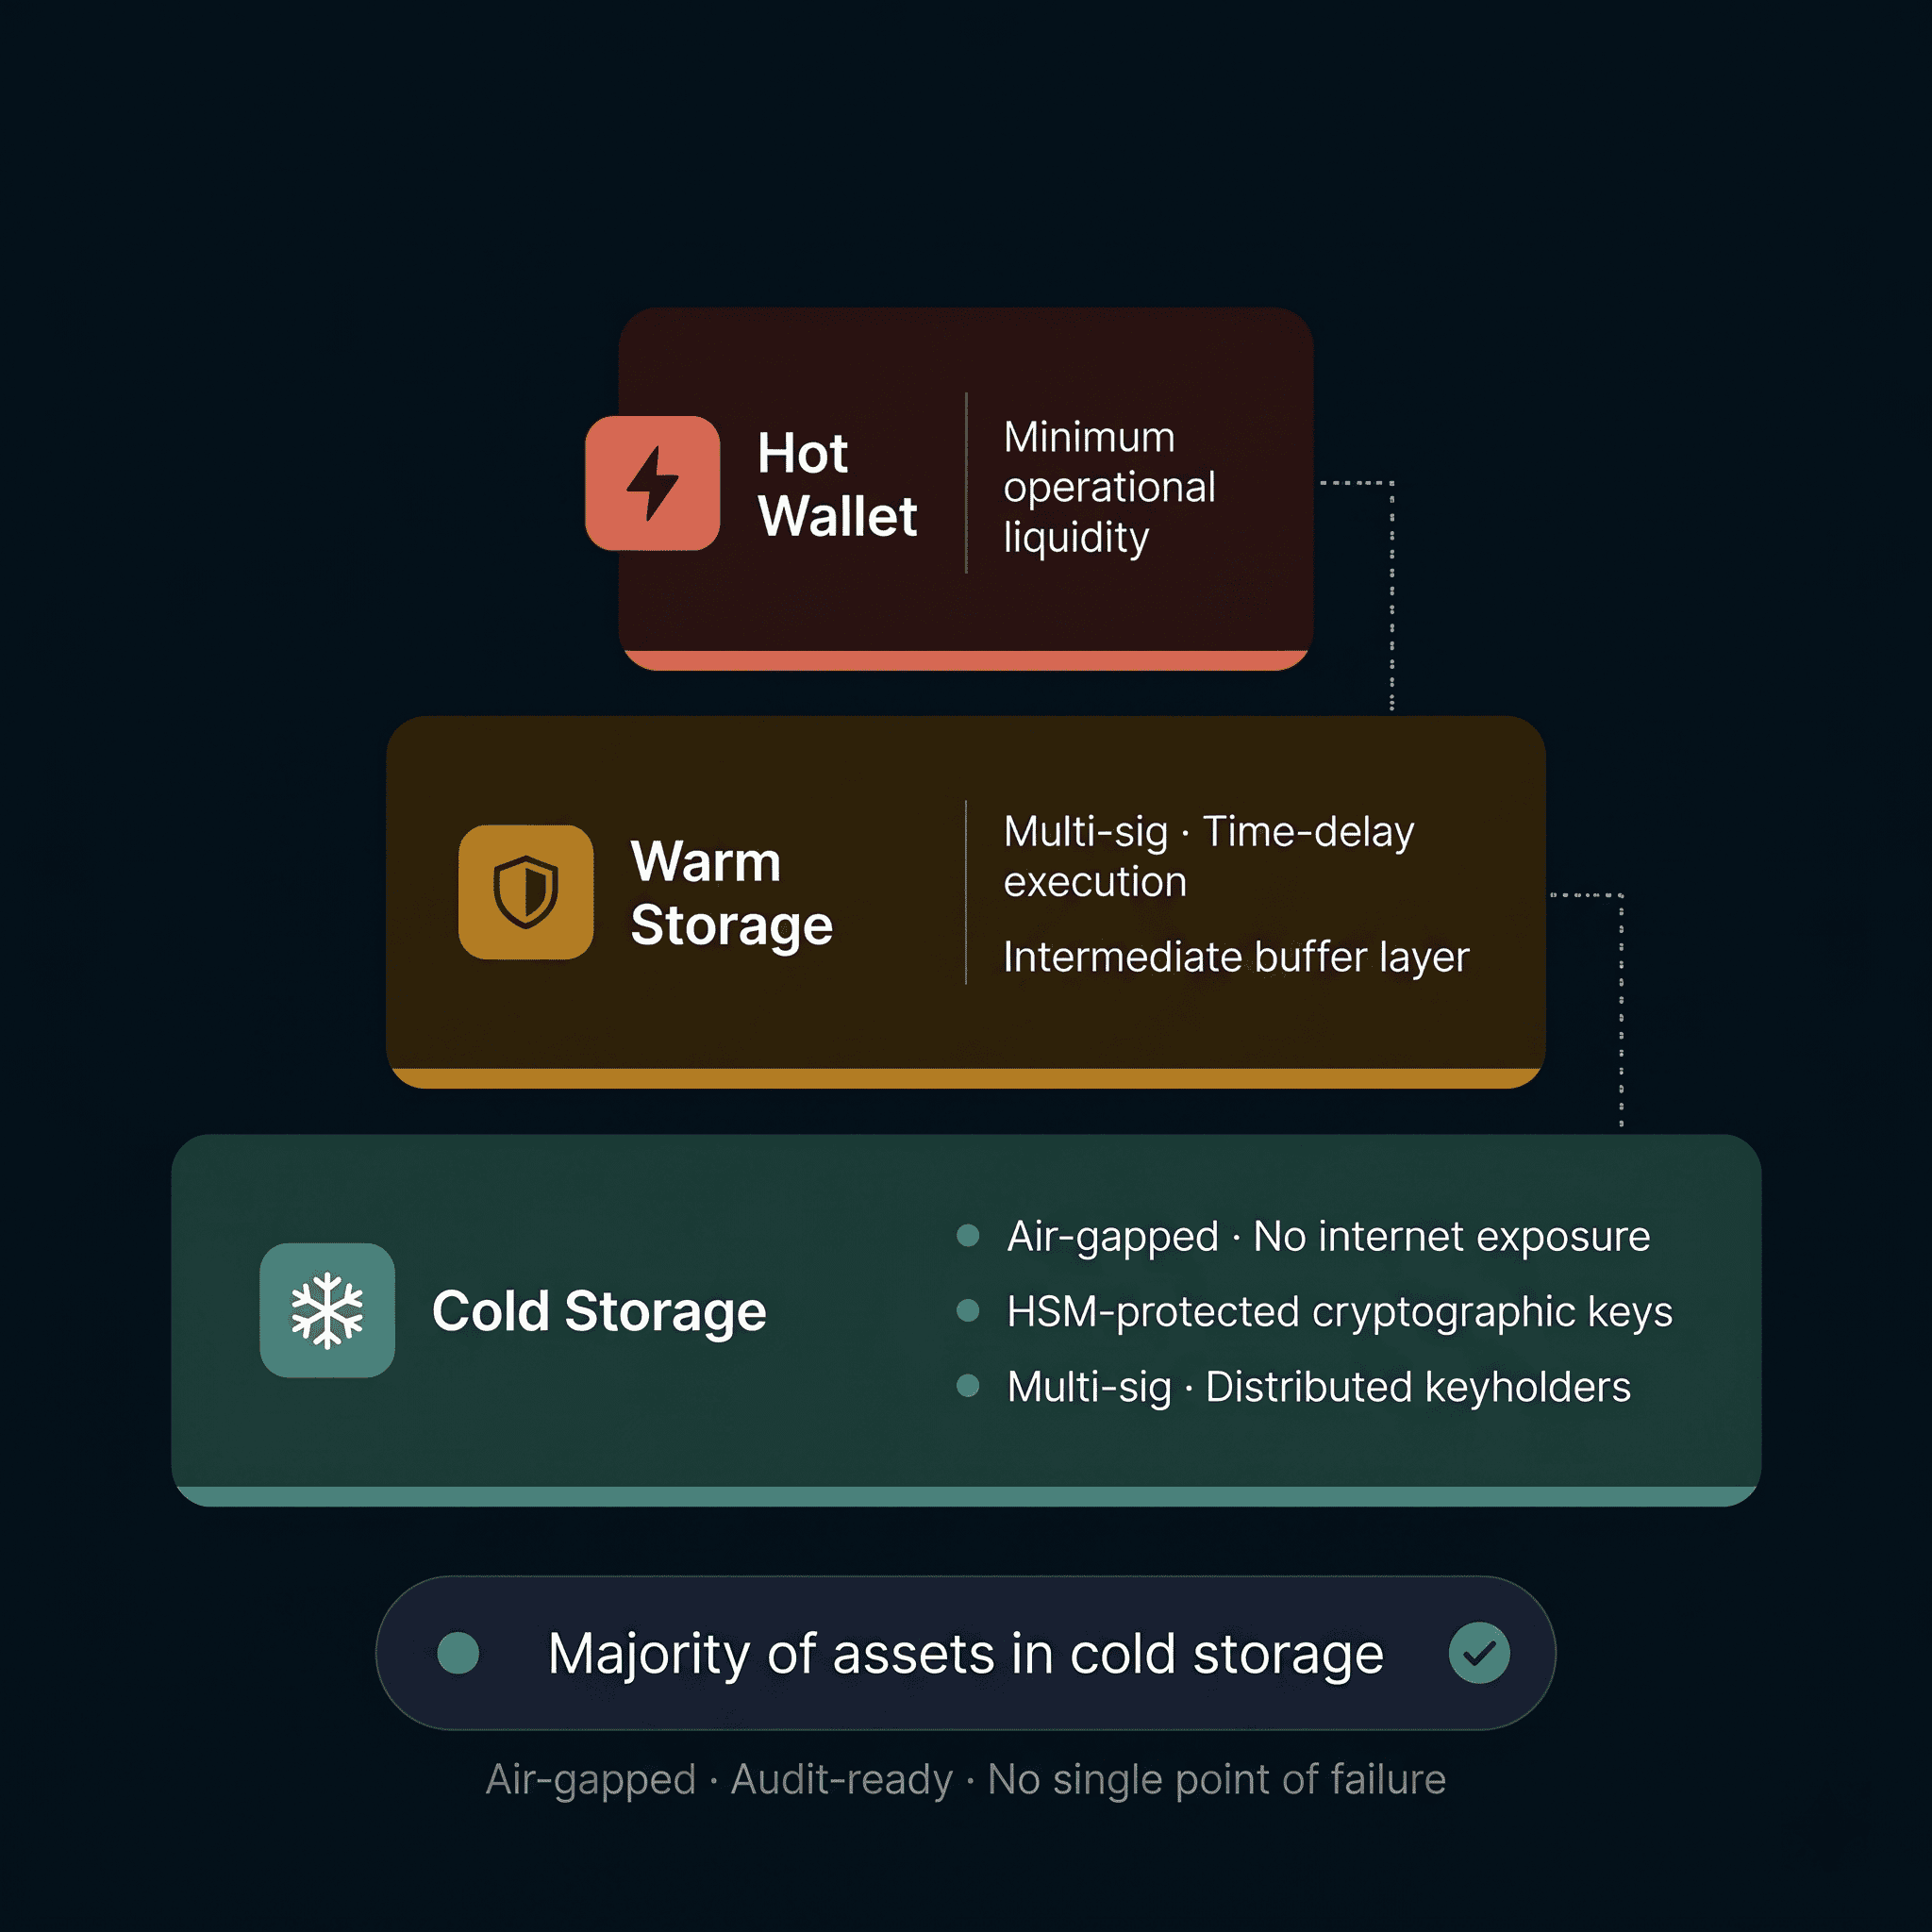
95%+ of all platform assets stored in air-gapped cold storage — never exposed to internet-connected infrastructure. HSM-protected, multi-signature authorization with geographically distributed keyholders. No single person, device, or facility can initiate a transfer unilaterally.
Minimum operational liquidity. Tightly capped with continuous outflow monitoring and automated rate limiting on anomalous withdrawal patterns.
Multi-signature access with time-delay execution. Intermediate buffer between operational funds and long-term cold reserves.
Air-gapped. HSM-protected. Multi-sig with distributed keyholders under configurable quorum rules. 95%+ of total platform assets reside here.
Exclusive Authenticated Control. The platform architecture ensures that internal development and operations teams cannot access, move, or redirect stored assets.
Architectural safeguards ensure only authorized operators can manage funds, preventing internal teams or unauthorized actors from accessing or moving assets.
Real-time auditing and logging provide a permanent record of all movements, enabling instant treasury reconciliation and automated compliance reporting.
Merkle tree-based Proof of Reserves with third-party attestation. Individual users cryptographically verify their balance is included in the platform's verified reserve total without exposing other users' data. Periodic auditor attestations ensure reserves equal or exceed total user deposits at all times. A verifiable cryptographic claim any user can check independently.
Advanced algorithms continuously monitor order book activity, execution patterns, and asset behavior.
Prevents external bots from exploiting market maker spreads and draining platform liquidity profits. Sub-millisecond execution controls neutralize arbitrage attacks that undermine operator revenue.
Security-first architecture protected by multi-layered firewalls, DDoS mitigation, and intrusion detection systems. Modular microservices with isolated environments limit attack surfaces and maintain uptime during peak activity.
Enterprise-grade volumetric attack absorption with intelligent traffic analysis and geographic edge distribution.
Blocks OWASP Top 10 vectors. Continuously updated rulesets from threat intelligence feeds.
Matching engine, custody, admin, and user services in isolated segments. Lateral movement architecturally prevented.
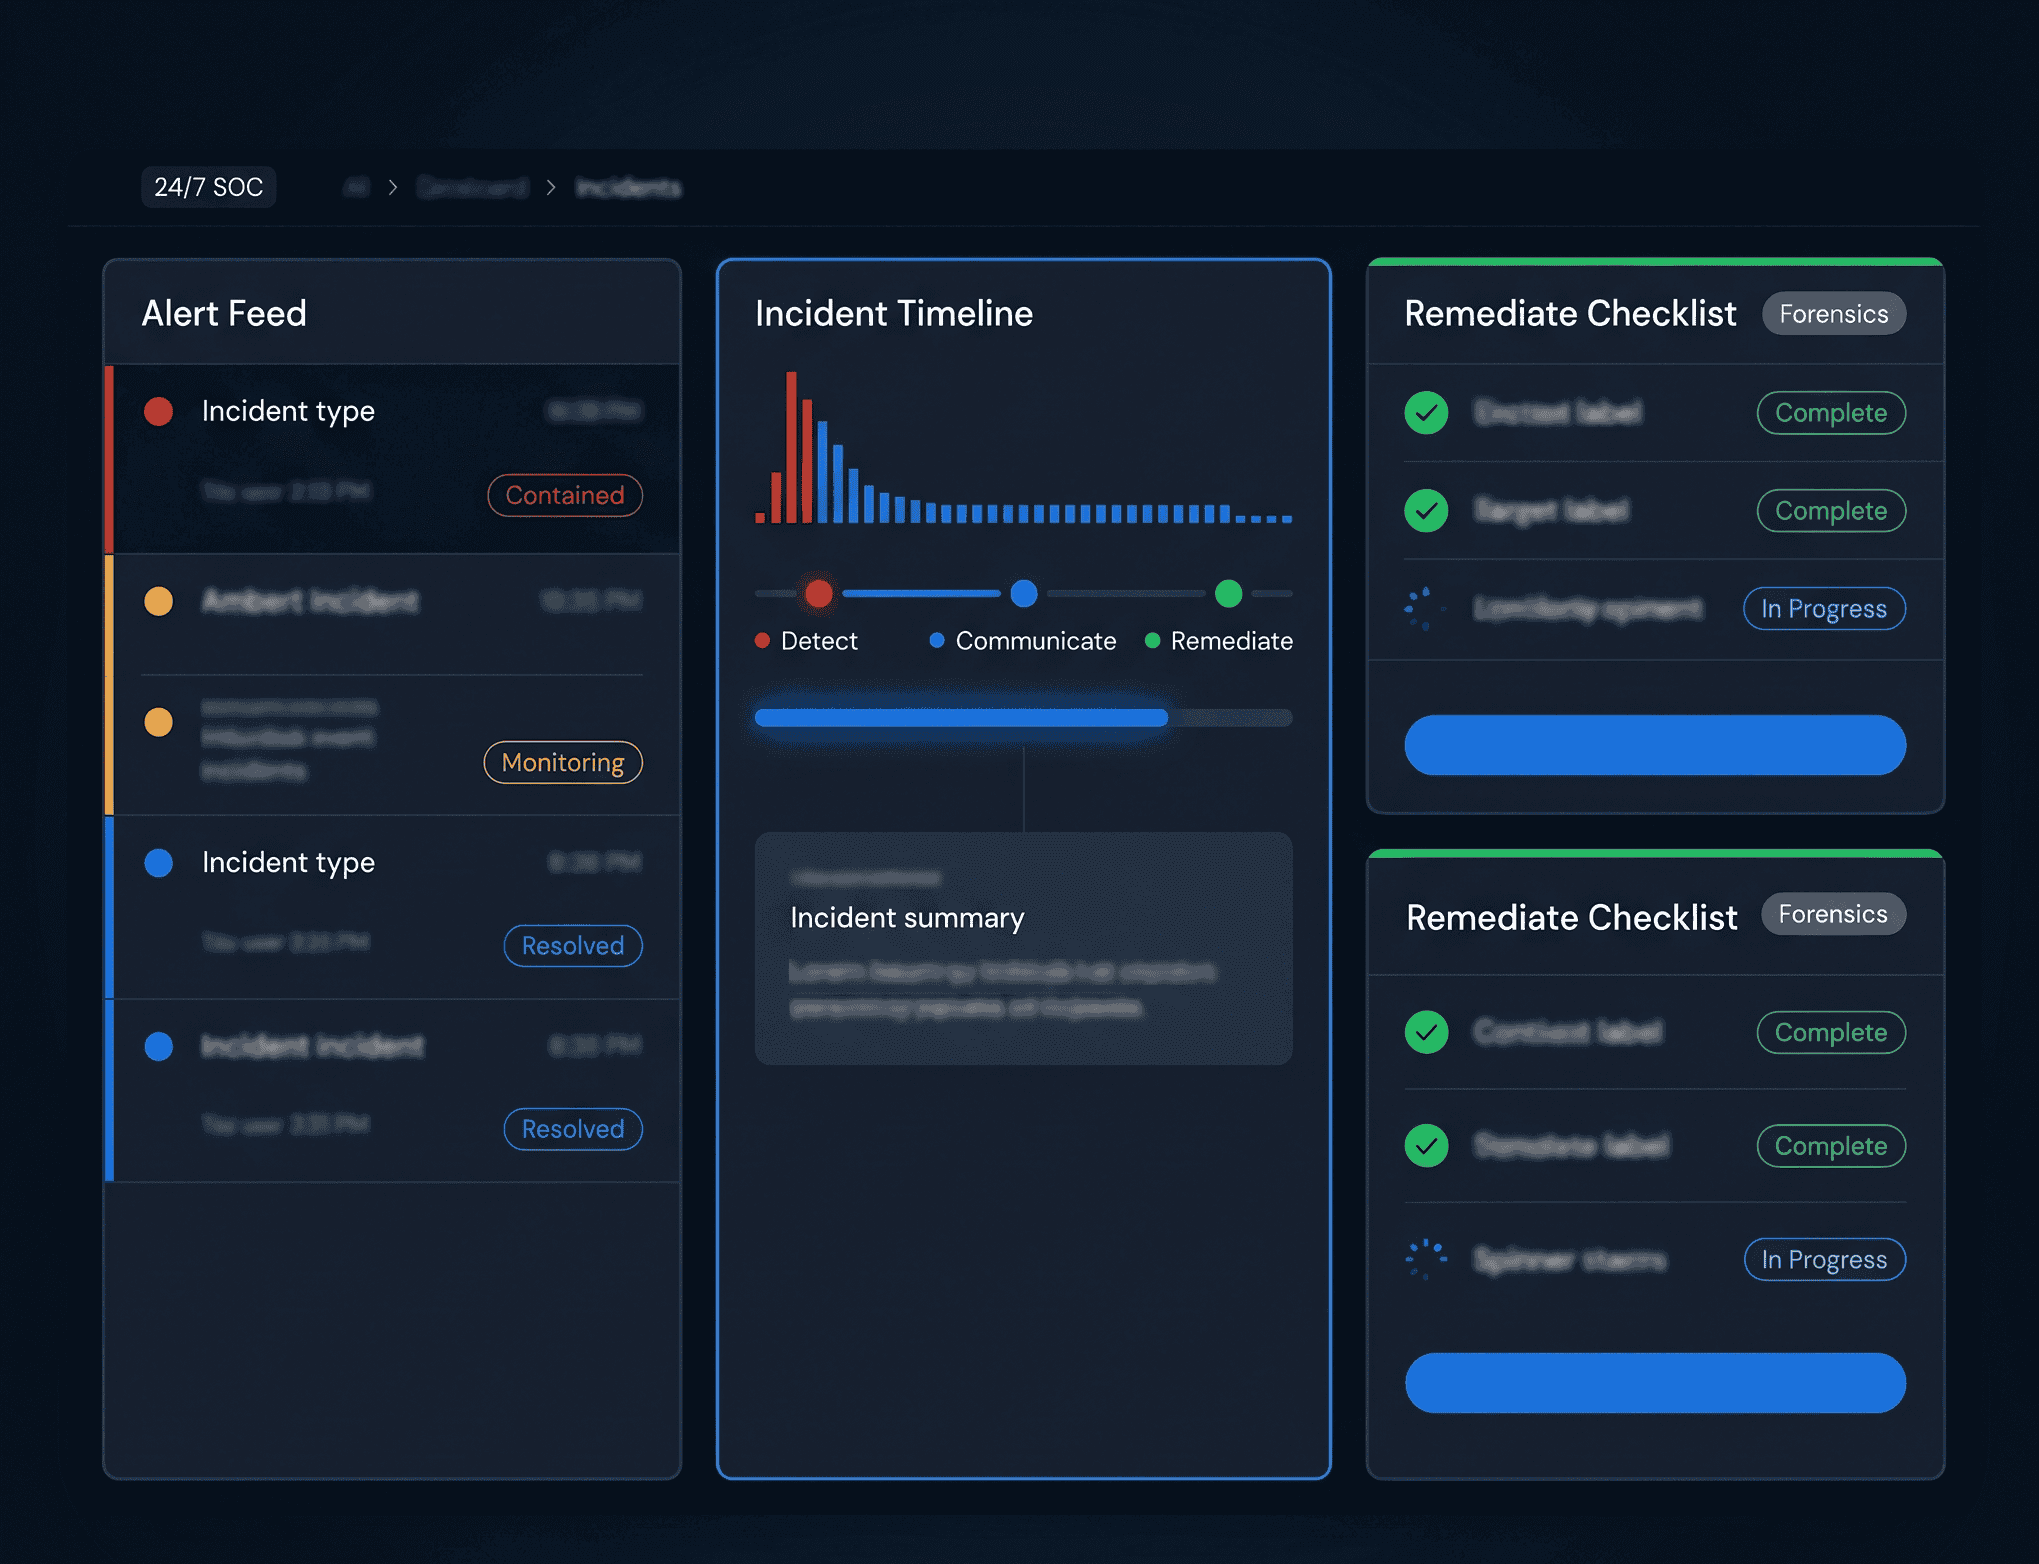
Real-time traffic and behavior monitoring with automated blocking. Integrated with 24/7 SOC.
Continuous automated scanning. Critical CVE patch SLA: under 24 hours.
An active disclosure programme pays external researchers for findings, so a bug reaches the security team rather than an exploit.
2FA (TOTP, SMS, email), biometric login (Face ID, Touch ID), FIDO2 hardware key support (YubiKey, Titan), and anti-phishing protections.
Operator teams access role-based access control (RBAC) with fine-tuned permissions. Every administrative action audit-logged with no shared credentials and no standing access to production systems beyond defined roles.
Every withdrawal passes through multiple automated security layers before approval.
Rigorous data handling standards to ensure privacy and regulatory compliance.
Only data required for compliance, security, and service delivery.
AES-256 on all PII and KYC records. Role-based access with full audit logging on every data access event.
Segregated environments. Production data never used in development or testing.
Regulatory-mandated durations only. Automated deletion on expiry or account closure.
Institutional API Security. Comprehensive protection for your exchanges API endpoints and developer ecosystem.
Independent reviews of app, infrastructure, custody, and API security with published remediation timelines.
Regular simulated attacks covering social engineering, network, application, and privilege escalation scenarios.
Active public program offering tiered rewards by severity, with accelerated remediation for reported issues.
95%+ in air-gapped cold storage with HSM and multi-signature quorum authorization. Operator-exclusive control — internal platform teams cannot access stored funds.
Address whitelisting with cooling periods, time-delayed large transactions, behavioral anomaly detection, user reputation scoring, and mandatory MFA on every withdrawal.
TOTP, SMS, email, biometric, and FIDO2 hardware keys. Anti-phishing protections, login monitoring, IP whitelisting, and device management. RBAC for operator teams.
Yes. Merkle tree-based PoR with third-party attestation — users cryptographically verify their balance is included in the verified reserve total.
Independent third-party audits, penetration testing, active bug bounty, and continuous vulnerability scanning with 24-hour critical patch SLA.
Architecture is one half of a security programme. These are the pages for the assessment that proves it holds, and the controls that sit beside it.
Review custody architecture, trading surveillance, compliance controls, and incident response.
Get Started